AI agents in SaaS were supposed to make software feel less like a dashboard and more like a teammate. Instead of clicking through endless menus, users could ask an agent to summarize churn risk, update a CRM record, draft a support reply, reconcile invoices, or trigger a workflow across several apps. That promise is still powerful, and it is exactly why founders, product teams, and enterprise buyers are moving fast. But the faster AI agents enter daily business software, the clearer one uncomfortable truth becomes: reliability is now the real bottleneck. The next wave of SaaS will not be judged only by how smart its agents sound, but by whether they can be trusted when the task actually matters.
The hype cycle around
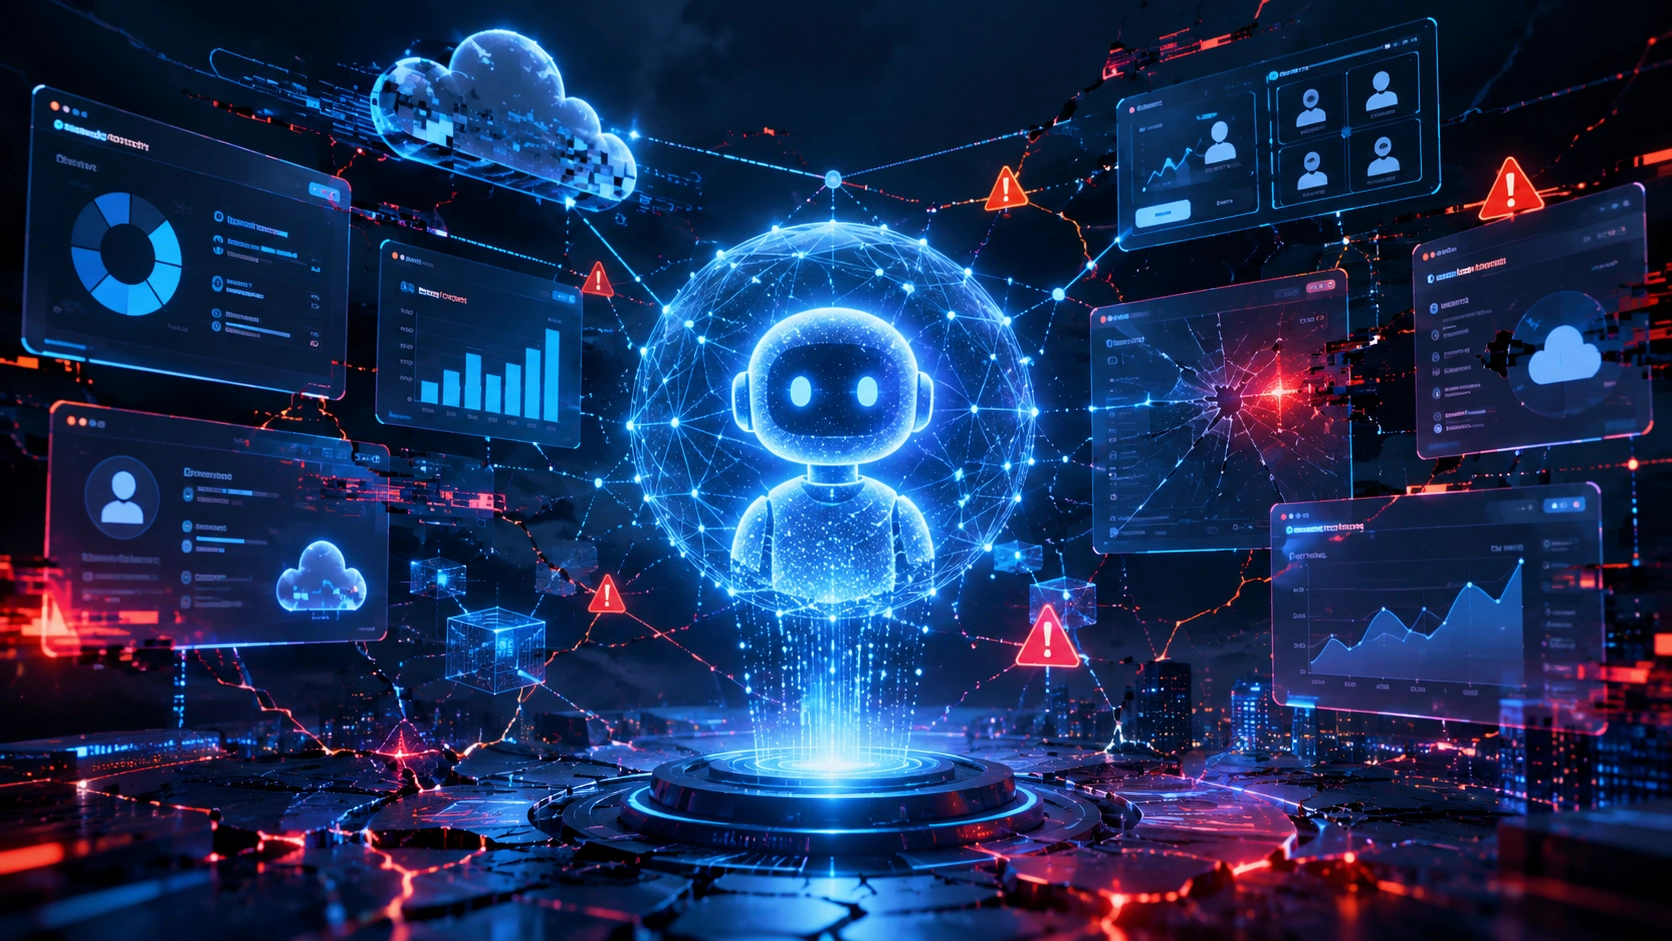
AI agents in SaaS has been loud, glossy, and full of big claims. Product demos show agents taking action across calendars, customer databases, ticketing systems, sales pipelines, finance tools, and cloud platforms with almost no friction. On stage, the agent looks calm, fast, and almost magical. In real workflows, though, a single misunderstood instruction can create a broken handoff, a wrong customer note, a risky permission change, or a confusing answer that sounds confident enough to pass unnoticed. That gap between demo magic and production reality is where the
AI reliability crisis is starting to hit SaaS companies.
Why AI Agents in SaaS Became the New Obsession
SaaS has always been about making work easier, but most software still asks users to do too much of the labor themselves. A dashboard may organize information, but the person still has to interpret the data, decide what matters, and push the next button.
AI agents change that pitch by promising to move from passive software to active software. They do not just display a sales opportunity; they can suggest the next action, write the follow-up, update the account, and schedule the call. For SaaS companies fighting feature fatigue, that shift feels like the cleanest way to make old products feel new again.
The market pressure is also very real. Buyers are asking every vendor what their AI roadmap looks like, even when they are not fully sure what they want from it. Investors are watching for signs that a SaaS company can defend its pricing power in an AI-first market. Founders are trying to avoid looking slow while newer startups package themselves as agent-native from day one. Product teams are being pushed to ship features that look more autonomous, more conversational, and more useful than traditional automation. In that climate, adding an agent can feel less like an experiment and more like a survival move.
But agents are not just another feature tab. A typical SaaS feature follows a narrow path, has predictable inputs, and gives users a visible way to confirm what is happening. An agent, by design, operates in a wider field of possibilities. It may read context, infer intent, call tools, generate text, make decisions, and trigger actions across systems. That flexibility is what makes the experience feel futuristic, but it is also what makes reliability harder to measure, harder to guarantee, and harder to explain when something breaks.
The Reliability Crisis Starts With Trust
Trust is the invisible contract behind every successful SaaS product. Users trust accounting software not to invent numbers, security platforms not to miss obvious threats, and CRM systems not to corrupt customer records. When software makes a mistake, users expect the mistake to be traceable, repeatable, and fixable. AI agents challenge that expectation because their behavior can feel less deterministic than traditional software. When the same prompt creates slightly different outcomes, users begin to ask whether the tool is helping them move faster or quietly adding new risk.
This is where the crisis becomes more serious than a few awkward chatbot replies. In low-stakes use cases, a clumsy agent response is annoying but manageable. In business-critical workflows, the cost can be much higher. An agent that misreads a contract clause, misunderstands a support escalation, or takes the wrong action inside an admin console can create real operational damage. The issue is not that AI agents fail all the time; it is that they can fail in ways that are subtle, confident, and difficult to catch before the mistake spreads.
For years, SaaS reliability meant uptime, latency, data consistency, and bug reduction. Those things still matter, but AI adds a new layer of reliability that is harder to monitor. A system can be online, fast, and technically healthy while still giving a poor answer or choosing a bad next step. That means engineering teams need to think beyond infrastructure metrics and start measuring reasoning quality, context accuracy, tool-call safety, and user outcome consistency. The new SaaS reliability stack is not only about keeping servers alive; it is about keeping decisions dependable.
Why Traditional QA Cannot Fully Catch Agent Failures
Traditional software testing works best when the product behavior is predictable. A team writes test cases, checks expected outputs, catches regressions, and ships improvements. That model becomes more complicated when an AI agent is expected to handle messy human language and unpredictable business context. Users do not always ask clean questions, and company data is rarely as neat as a demo environment. An agent may pass a controlled test suite and still struggle when it meets real customer tickets, incomplete CRM fields, conflicting policies, or ambiguous instructions.
The bigger problem is that agent failures are often qualitative. A wrong API response is easy to detect when a field does not match the schema. A weak agent response may be technically valid while still being strategically wrong, tone-deaf, incomplete, or risky. It can write a support message that sounds polite but ignores the actual issue. It can summarize a sales call in a way that feels clean but misses the buying objection that mattered most. These are not classic bugs, but they still damage the user experience and weaken confidence in the product.
Evaluation also gets harder as agents gain more autonomy. A simple AI assistant that only drafts text can be reviewed before anything goes out. An agent that can execute actions needs stronger guardrails because the output is no longer just language. It might change records, move files, create tickets, send messages, or trigger integrations. Every additional permission expands the surface area for mistakes, which means SaaS companies need evaluation systems that test not only what the agent says, but what it does after it says it.
Enterprise Buyers Are Excited, but Not Careless
Enterprise customers are not rejecting AI agents outright. Many teams genuinely want software that reduces busywork, speeds up analysis, and helps employees focus on higher-value decisions. The demand is real because modern companies are drowning in tools, meetings, tickets, alerts, and internal data. A reliable agent that can cut through that noise has obvious business value. The issue is that enterprise buyers have learned to separate impressive AI demos from dependable production systems.
Procurement teams are already asking tougher questions. They want to know what data the agent can access, how permissions are enforced, how outputs are logged, and whether sensitive information can leak across workflows. Security teams want audit trails, role-based access, retention controls, and clear incident paths. Legal teams want to understand how AI-generated actions are reviewed and who is responsible when something goes wrong. In other words, the agent may be the shiny feature, but governance is what determines whether the deal actually closes.
This creates a new competitive divide in
SaaS. Vendors that treat agents like a cosmetic chatbot layer may win attention but lose trust during deeper evaluations. Vendors that design agents around permissions, observability, review flows, and measurable accuracy will have a stronger chance of becoming long-term enterprise platforms. The market is moving past the question of whether AI can produce impressive outputs. The sharper question now is whether AI can operate safely inside complicated organizations without becoming a liability.
The Hidden Risk of Over-Automating Workflows
One of the most tempting ideas in AI SaaS is full automation. The dream is simple: let the agent handle repetitive work from start to finish while humans supervise only the exceptions. That sounds efficient, especially for teams under pressure to do more with fewer resources. But full automation can become dangerous when companies skip the boring middle stage of partial trust. Before an agent can safely own a workflow, it needs to prove that it can handle edge cases, uncertainty, and conflicting instructions without quietly making things worse.
There is also a human behavior problem. When users see an AI agent succeed several times, they may begin to trust it more than they should. They stop checking details, skim approvals, and assume the system probably handled the task correctly. This is not laziness; it is how people adapt to tools that appear reliable. The danger is that one rare but serious failure can slip through because the user has already learned to treat the agent as dependable.
Smart SaaS companies are starting to design around this reality. They are building confidence levels, approval steps, restricted action modes, rollback options, and clearer explanations of why an agent made a recommendation. They are also separating low-risk tasks from high-risk tasks instead of treating all automation as equal. Drafting a meeting summary is not the same as changing a billing record or modifying a security setting. The best AI SaaS products will understand that autonomy should be earned gradually, not granted all at once because the demo looked smooth.
Security and Compliance Make the Crisis Bigger
Reliability is not only about accuracy. In SaaS, it is also connected to
cybersecurity, compliance, and data governance. AI agents often need access to sensitive information to be useful, which means they may touch customer records, financial data, internal documents, code repositories, or operational systems. The more context an agent can read, the more helpful it becomes. At the same time, every new access path creates another place where permission design can fail.
This is especially tricky because agents can combine information from multiple systems. A human employee may understand that some data should not be copied into a public channel or shared with a vendor. An AI agent needs that boundary to be designed, enforced, and tested. If it pulls private details into a generated email or summarizes restricted information for the wrong audience, the mistake can become a compliance issue. SaaS companies cannot rely on good intentions when the product is operating inside regulated or high-trust environments.
Security teams are also worried about prompt injection, malicious inputs, and tool abuse. If an agent reads external content, that content may contain instructions designed to manipulate its behavior. If the agent can call tools, attackers may try to trick it into taking actions the user never intended. This turns AI reliability into a security discipline, not just a product quality concern. A SaaS agent that cannot defend its own instruction hierarchy is not ready for serious enterprise autonomy.
What Reliable AI SaaS Actually Looks Like
Reliable AI SaaS does not mean an agent is perfect. No serious team should promise that. Reliability means the system is designed to know its limits, handle uncertainty honestly, and reduce the chance of harmful outcomes. A good agent should ask for clarification when the task is ambiguous, refuse actions it is not authorized to take, and show users what it is about to do before it does something sensitive. The product should make trust visible instead of asking users to believe in a black box.
Observability will become a major part of this shift. SaaS teams need to see how agents behave across real workflows, not just lab tests. They need logs that show inputs, retrieved context, tool calls, decisions, and final outputs in a way that can be audited. They need evaluation dashboards that track failure patterns, not just usage growth. If an agent is used thousands of times a day, the company needs to know where it struggles, which customers are affected, and which tasks should be restricted until performance improves.
Another important piece is human control. The strongest products will not frame humans as obstacles to automation. They will frame humans as reviewers, trainers, and decision owners. In many workflows, the right product pattern is not “agent does everything,” but “agent prepares the work and the human approves the final move.” That model may sound less flashy, but it is often the version that enterprises can actually adopt without creating unnecessary risk.
The Business Impact for SaaS Startups
For SaaS startups, the reliability crisis creates both danger and opportunity. The danger is that shipping a weak agent too quickly can damage credibility before the company has time to mature. Early users may forgive missing features, but they are less forgiving when a product makes confident mistakes inside important workflows. A startup that becomes known for unreliable automation may struggle to win serious customers later. In a crowded AI market, trust can become a stronger moat than speed.
The opportunity is that reliability itself can become a product advantage. Startups do not need to beat larger platforms by claiming their agents can do everything. They can win by doing a narrower set of tasks extremely well, with clear permissions, strong review flows, and measurable outcomes. A focused vertical agent for legal intake, healthcare admin, finance reconciliation, or customer support escalation may be more valuable than a broad assistant that handles everything poorly. The next generation of SaaS winners may be the companies that choose precision over spectacle.
Pricing could change too. If agents reliably complete work that previously required human labor, vendors may move away from seat-based pricing and toward outcome-based or usage-based models. But that shift only works if customers believe the output is dependable. Nobody wants to pay premium prices for automation they must constantly double-check. The more a SaaS company ties pricing to AI productivity, the more it must prove that the agent is not just active, but accurate, safe, and worth trusting.
The Practical Playbook for SaaS Teams
The first practical move is to stop treating agents as a single feature and start treating them as a system. That system includes the model, the data layer, the permissions layer, the workflow engine, the user interface, the audit trail, and the evaluation process. If one part is weak, the whole agent experience becomes fragile. A beautiful chat interface cannot compensate for poor context retrieval or unclear action boundaries. SaaS teams need to design the entire loop, from user request to final outcome.
The second move is to classify tasks by risk. Low-risk tasks can be more autonomous because the cost of failure is small. Medium-risk tasks may need user confirmation, explanation, or easy rollback. High-risk tasks should require stricter approval, tighter permissions, and more detailed logging. This kind of risk-based design may not sound as exciting as saying an agent can run the whole company, but it is much closer to how real businesses adopt new technology.
The third move is to build evaluation into the product lifecycle. Teams should test agents against real-world scenarios, edge cases, adversarial prompts, messy data, and domain-specific judgment calls. They should not rely only on generic benchmarks because SaaS workflows are deeply contextual. A customer support agent, a finance agent, and a cloud operations agent all fail in different ways. The companies that understand those failure modes early will have a much stronger product foundation than teams that only test whether the agent gives a nice answer.
Why the Best SaaS Agents Will Feel Less Flashy
There is a funny twist in the AI agent race. The most reliable agents may not always look the most impressive in a quick demo. They may pause more often, ask better questions, show more warnings, and limit what they can do without approval. That can make them feel less cinematic than an agent that instantly takes action across a dozen tools. But in real business environments, restraint is not a weakness; it is a sign that the product understands the stakes.
This is the difference between a toy and infrastructure. A toy is allowed to surprise people because the consequences are small. Infrastructure has to be boring in the best possible way. It needs to work consistently, fail safely, and help users understand what happened. If AI agents are going to become part of the SaaS operating layer, they need to earn that boring kind of trust.
That does not mean the future of SaaS will be less exciting. It means the excitement will move from raw generation to dependable execution. The most valuable products will not simply answer questions; they will complete workflows with enough transparency that teams can rely on them. They will help employees move faster without making them feel like they are babysitting a risky system. That is a harder goal than a slick demo, but it is also a much bigger business.
Conclusion: Reliability Is the New SaaS Moat
The rise of
AI agents in SaaS is not slowing down, but the conversation is maturing fast. The first phase was about excitement, novelty, and the feeling that software could finally understand what users wanted. The next phase is about reliability, governance, and whether agents can perform inside real businesses without creating hidden chaos. Companies that ignore this shift may ship fast but lose trust when customers discover the system is not ready for serious work. Companies that take reliability seriously can turn safety, transparency, and dependable execution into a competitive advantage.
The reliability crisis does not mean AI agents are doomed. It means SaaS is entering the part of the cycle where the technology has to grow up. Users do not need agents that act confident all the time; they need agents that are useful, honest, controlled, and accountable. The winners will be the platforms that understand when to automate, when to ask, when to explain, and when to stop. In the end, the future of SaaS will belong not to the loudest AI agent, but to the one people can actually trust with their work.